When your systems age or grow, sadly, so do your risks — even if you don’t realise it.
Security gaps often develop gradually. New users are added, software changes, access expands and systems evolve — while older settings and controls can remain in place unnoticed.
Sometimes those gaps only become visible when a customer asks for evidence of your security, an audit takes place or something suspicious happens.
Talk to our team
Security needs more than antivirus
For many businesses, security is not something that has been designed from the beginning as one complete system. Controls are added over time as the business changes.
Users are added, access requirements grow, new applications are introduced and devices are replaced. The risk is that older settings, excessive access or gaps in protection remain unnoticed.
Some of the issues we commonly look for include:
- Default settings that have never been reviewed
- Access that is broader than it needs to be
- New systems introduced without appropriate security controls
- Devices that are not properly maintained or patched
- Limited visibility over suspicious activity
- No clear understanding of what is being protected
- No defined response when something suspicious is detected
The objective is not to add as many security products as possible. We first look at what you already have, what is working and where the genuine gaps are.
Security should continue to evolve as your business changes.
A layered approach to security
Good security does not depend on one product. We look across identities, devices, email, networks, web access and your people so that the different controls work together.
Identity security
We help secure Microsoft 365 and Entra ID identities using controls such as Multi-Factor Authentication, Conditional Access and identity threat detection.
Where suspicious account activity is detected, appropriate response actions can be taken to reduce the risk of unauthorised access.
Endpoint security
We protect supported computers using Microsoft Defender together with Huntress EDR, alongside patching, vulnerability management and ongoing monitoring.
Where suspicious activity is identified, we investigate and remediate the issue rather than relying only on traditional antivirus.
Network security
Where appropriate, we design and manage business firewall and network security using solutions such as Sophos.
This can include firewall configuration, remote access, VPNs, firmware management and security rules appropriate to the environment.
Email security
Microsoft 365 provides important email security controls, and where additional filtering is required we can use services such as MailGuard.
The objective is to reduce malicious, unwanted and suspicious email before it reaches your users.
Web and DNS protection
Where appropriate, DNS filtering can be used to restrict access to known malicious, phishing and inappropriate websites.
This provides another protection layer before users connect to risky destinations.
Security awareness training
Technology is only part of security. We can provide ongoing Security Awareness Training and simulated phishing exercises to help staff recognise common threats and develop better security habits.
The purpose is education and improvement — not catching people out.
Monitoring matters as much as prevention.
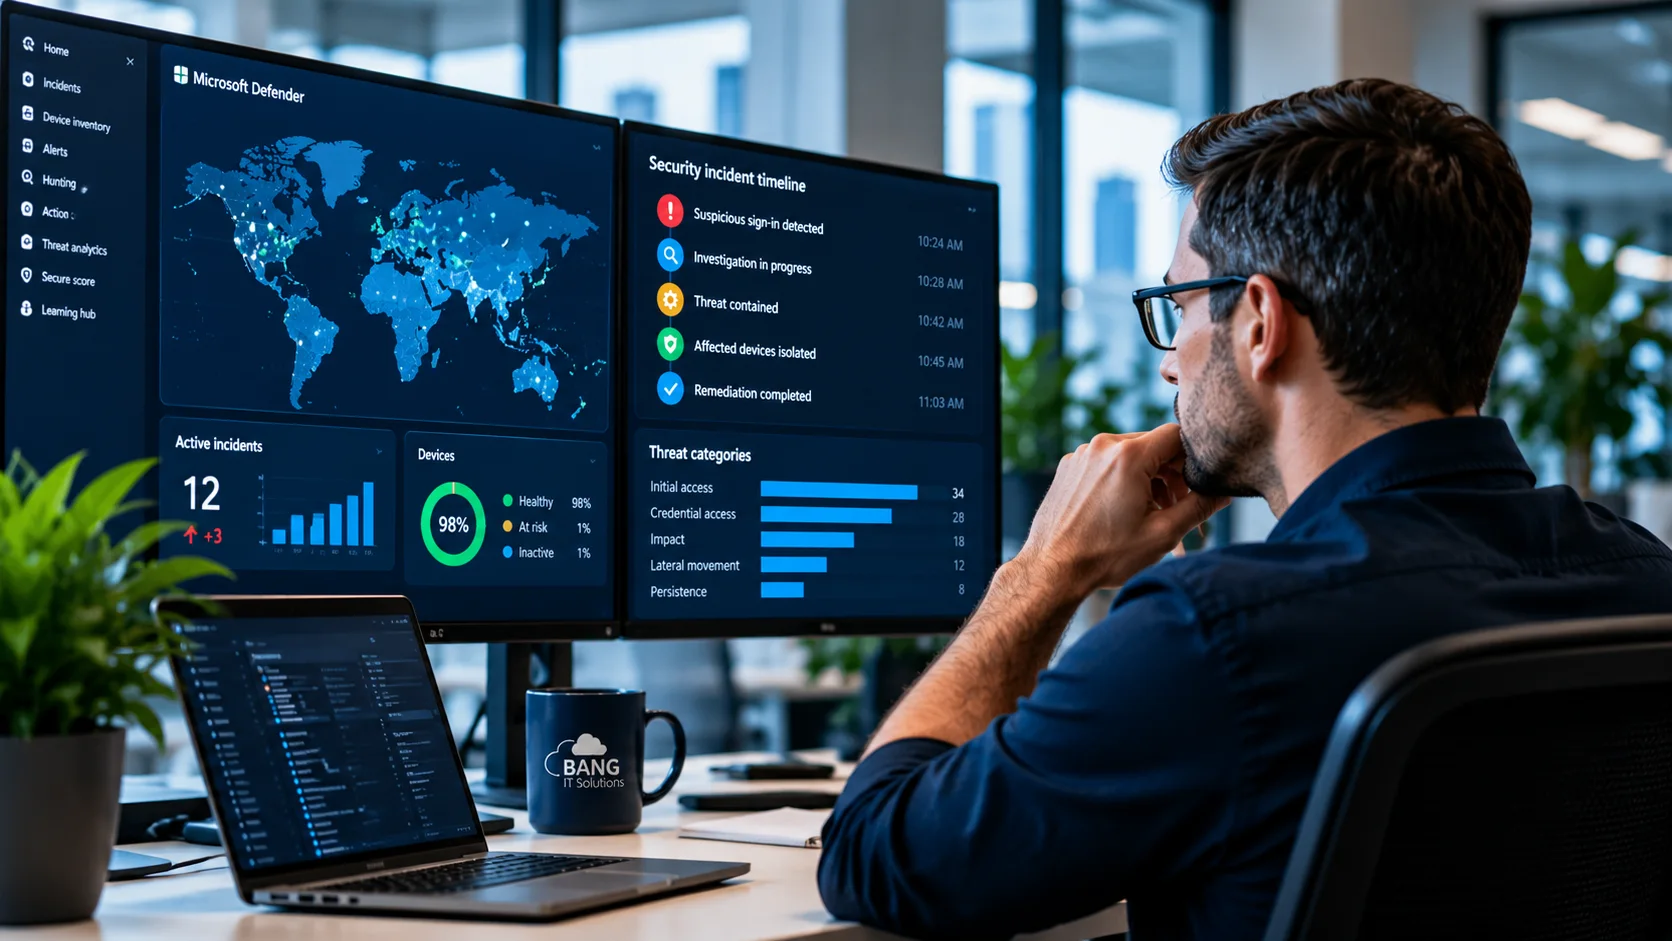
No security product can guarantee that every threat will be stopped. Monitoring gives us visibility when something suspicious does happen so that it can be investigated and acted on.
Our managed security approach uses Microsoft security capabilities together with services such as Huntress to monitor supported devices and identities, investigate genuine threats and take appropriate action.
Detect
Suspicious activity is identified across supported devices, identities or security systems.
Investigate
Alerts are reviewed to determine what happened, the likely cause and the potential impact.
Contain
Where necessary, action can be taken to limit the impact — such as isolating a device, disabling an account, revoking sessions or blocking malicious activity.
Remediate
We remove or resolve the issue, restore normal operation where required and address the underlying cause where practical.
Security reduces risk. Backups give you a recovery path.
Even with strong security in place, things can still go wrong. Security helps reduce the likelihood and impact of an incident; backups give you another recovery option when data needs to be restored.
We manage Microsoft 365 backups for managed clients and can discuss backup requirements for other systems where appropriate.
Explore Backup & RecoveryCyber Security and Managed IT
Many of these protections form part of the technology environment we manage for our Managed IT clients.
Additional requirements such as firewall projects, security reviews or remediation work can be scoped separately where needed.
Explore Managed IT ServicesFrequently Asked Questions
Is antivirus enough for a business?
Antivirus is an important layer, but it is not enough on its own. Modern attacks also target user identities, email, cloud services, unpatched software and legitimate access credentials.
A stronger security approach combines prevention with monitoring, identity protection, endpoint security and a clear response process.
Do you monitor security outside normal business hours?
Some of the security services we use include continuous monitoring and 24/7 Security Operations Centre capabilities.
That does not mean Bang IT operates a 24/7 helpdesk. Normal IT support remains subject to the support arrangements agreed with each client.
What happens if one of our Microsoft 365 accounts is compromised?
The response depends on what has occurred. Actions may include disabling or securing the account, resetting credentials, revoking active sessions, reviewing sign-in activity and investigating the affected environment.
We then work through the cause and any additional remediation that is required.
Do we need to replace our existing firewall or security products?
Not necessarily. We prefer to review what you already have before recommending changes.
If an existing product is appropriate, supportable and properly configured, there may be no reason to replace it simply for the sake of standardisation.
Do you provide Security Awareness Training?
Yes. Security Awareness Training and simulated phishing can be used to help staff recognise suspicious activity and improve security habits over time.
Can you guarantee we will never have a cyber incident?
No security provider or product can guarantee that an incident will never occur.
The objective is to reduce risk, improve visibility, respond appropriately when something happens and maintain suitable recovery options.
Talk to us about your security setup.
Whether you’re concerned about Microsoft 365 accounts, endpoint security, your firewall or simply want to know whether your current setup is appropriate, we can talk through what you have in place and recommend sensible next steps.
Talk to our team